在此頁面上:瞭解如何建立API認證、選擇驗證方法,以及設定標頭、裝載和輸入設定來傳送SMS和RCS訊息,以整合Adobe Journey Optimizer中的自訂訊息提供者。
此功能可讓您整合及設定自己的傳訊提供者,除了預設選項(Sinch、Twilio和Infobip)以外,還提供了彈性。 如此一來,行動訊息就能順暢地撰寫、傳送、報告和同意管理。
透過自訂提供者設定,您可以直接在Journey Optimizer中連線協力廠商傳訊服務、自訂動態內容的訊息裝載,以及管理選擇加入/選擇退出偏好設定,以確保在SMS和RCS通道間保持一致。
若要設定自訂提供者,請遵循下列步驟:
建立您的 API 認證 api-credential
若要在Journey Optimizer中使用Adobe未提供的現成自訂提供者(例如Sinch、Infobip、Twilio)傳送行動訊息,請遵循下列步驟:
-
在左側邊欄中,瀏覽至管理
>管道,選取 簡訊設定 下的 API認證 功能表,然後按一下 建立新的API認證 按鈕。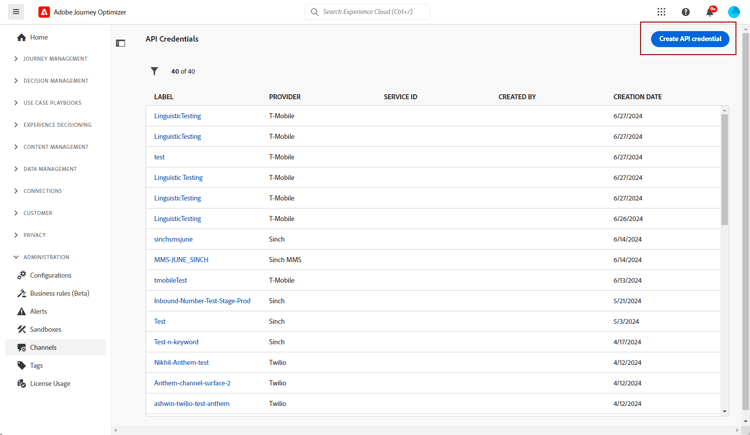
-
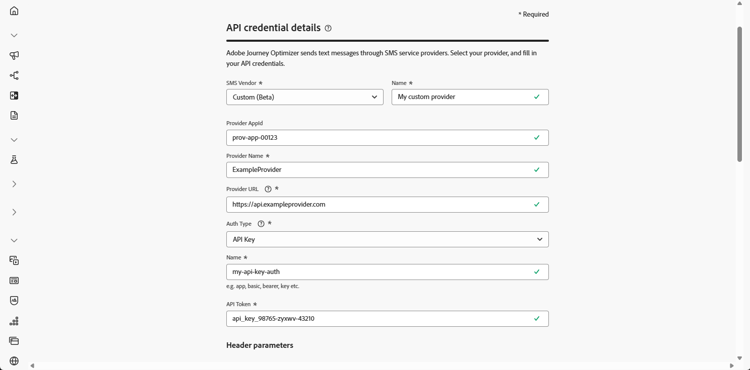
設定您的SMS API認證,如下所述:
-
SMS供應商:自訂。
-
名稱:輸入您的API認證名稱。
-
提供者AppId:輸入您的SMS提供者提供的應用程式ID。
-
提供者名稱:輸入您的SMS提供者的名稱。
-
提供者URL:輸入簡訊提供者的URL。
-
頻道型別:選擇性。 指出此認證代表的行動裝置頻道,即SMS、RCS或MMS。
-
驗證型別:選取您的授權型別,並根據選取的驗證方法完成對應的欄位。
-
-
啟用 mTLS支援 選項,以確保使用者端和伺服器在建立安全連線之前互相驗證。
若要僅使用mTLS,請從 驗證型別 下拉式清單中選取無驗證,然後啟用mTLS支援。
請注意,mTLS僅適用於SMS提供者(訊息傳送)端點。 OAuth權杖端點不得使用mTLS。 在測試之前,請確定已在權杖端點上停用mTLS。
note important IMPORTANT 透過從MTLS公用憑證API下載公用憑證,並將它新增至您的伺服器信任存放區(預期的使用者端CN: ajo-sms.aep-mtls.adobe.com),將您的SMS傳送端點設定為信任Adobe Experience Platform憑證授權鏈結,否則Journey Optimizer會省略使用者端憑證,SMS傳送會失敗。 -
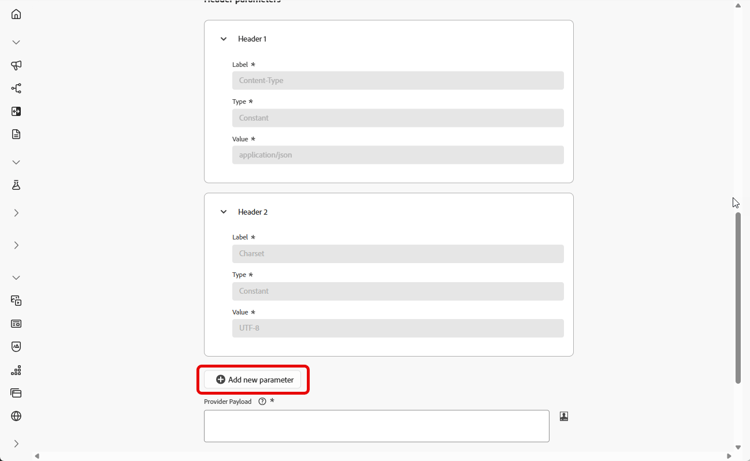
在 標頭 區段中,按一下 新增引數 以指定將傳送給外部服務的要求訊息的HTTP標頭。
Content-Type和 Charset 標頭欄位是預設設定,無法刪除,不過您可以編輯預設的 Content-Type 值。 您可以新增最多10個自訂標頭引數。
-
新增您的提供者裝載,以驗證及自訂您的要求裝載。
對於RCS訊息,此承載稍後會在內容設計期間使用。
note NOTE 設定具有基本或持有者驗證的自訂SMS提供者時,您必須在JSON裝載中包含 authOption引數。 此外,提供者承載必須參考範本變數{{fromNumber}}、{{toNumber}}和{{message}}。提供者承載也支援Adobe Journey Optimizer 個人化協助程式功能,包括 encode64。 -
選取使用傳入的自訂資料集,將此認證的傳入SMS路由至您從下拉式清單中選擇的預先建立資料集。 進一步瞭解如何使用傳入關鍵字的自訂資料集
note NOTE 資料集結構描述必須是XDM ExperienceEvent,而且至少包含下列欄位群組: - Adobe CJM ExperienceEvent — 訊息互動細節
- Adobe CJM ExperienceEvent — 訊息執行詳細資料
- Adobe CJM ExperienceEvent — 訊息設定檔詳細資料
必須為設定檔啟用結構描述和資料集。 -
完成API認證的設定時,請按一下提交。
-
在 API認證 功能表中,按一下

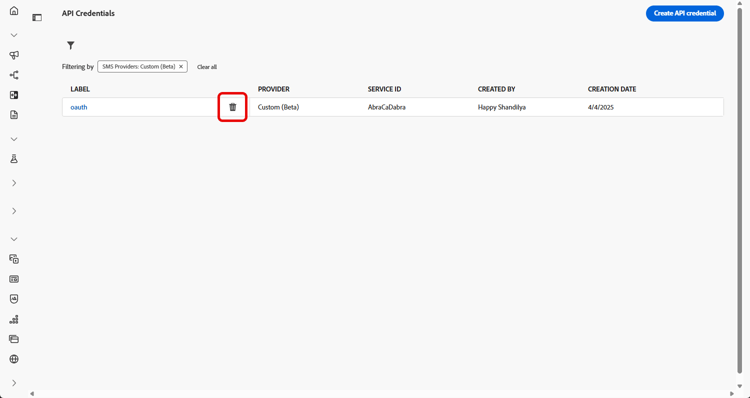
-
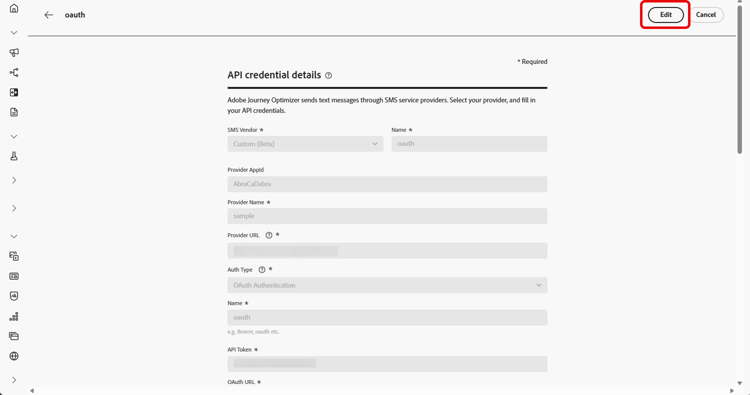
若要修改現有認證,請找到所需的API認證,然後按一下 編輯 選項以進行必要的變更。
-
從您現有的API認證按一下驗證SMS連線,透過傳送範例訊息至指定裝置來測試及驗證SMS API認證。
-
填寫 數字 和 訊息 欄位,然後按一下驗證連線。
note important IMPORTANT 訊息的結構必須符合提供者的裝載格式。 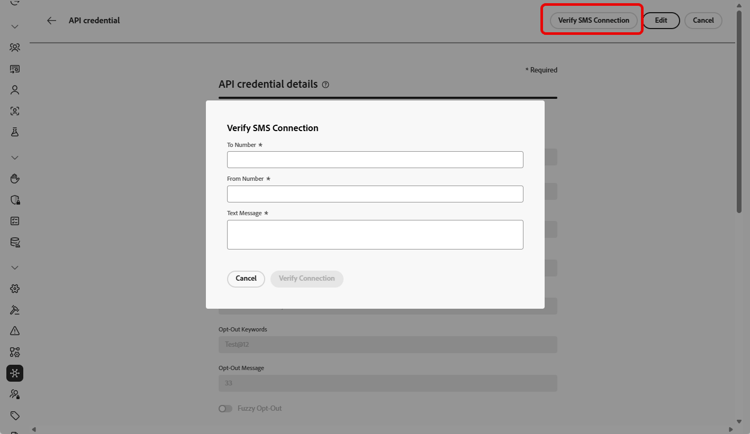
在建立及設定您的API認證後,您現在需要為Webhook🔗設定簡訊的傳入設定。
自訂 SMS 提供者的驗證選項 auth-options
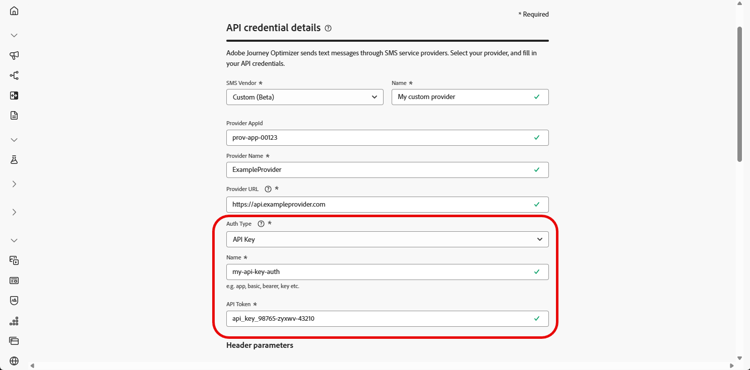
建立API認證後,請完成API金鑰驗證所需的欄位:
- 名稱:輸入API金鑰組態的名稱。
- API Token:輸入您的SMS提供者提供的API Token。
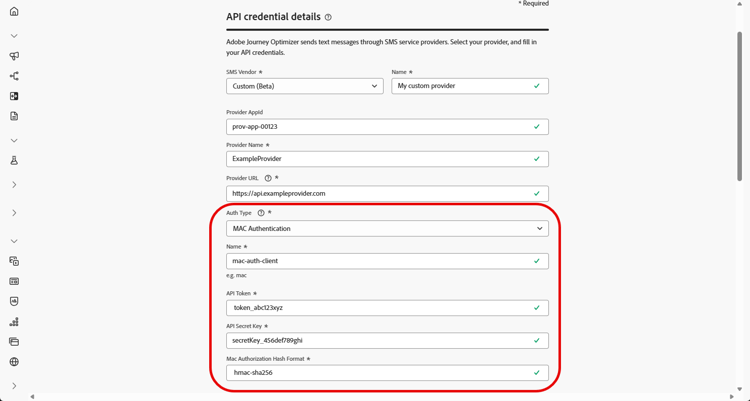
建立API認證後,請完成MAC驗證所需的欄位:
- 名稱:輸入MAC驗證組態的名稱。
- API Token:輸入您的SMS提供者提供的API Token。
- API秘密金鑰:輸入您的SMS提供者提供的API秘密金鑰。 此金鑰用於產生MAC (訊息驗證代碼),以進行安全通訊。
- Mac授權雜湊格式:選擇MAC驗證的雜湊格式。
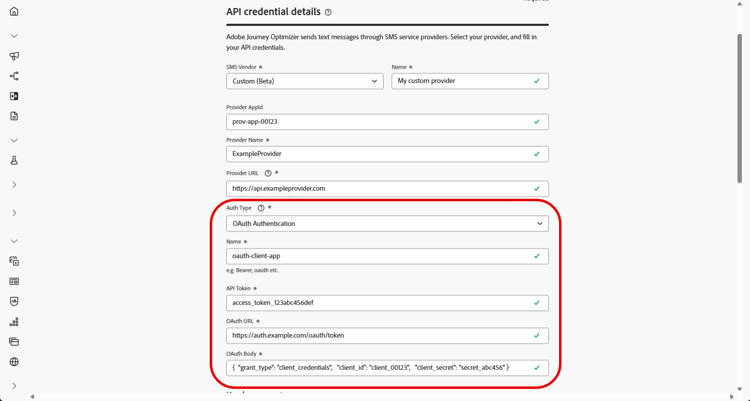
建立API認證後,請完成OAuth驗證所需的欄位:
-
名稱:輸入您OAuth驗證組態的名稱。
-
API Token:輸入您的SMS提供者提供的API Token。
-
OAuth URL:輸入用於取得OAuth權杖的URL。
-
OAuth內文:提供JSON格式的OAuth要求內文,包括
grant_type、client_id和client_secret等引數。
Journey Optimizer會在自訂SMS聯結器到期時動態重新整理OAuth權杖。
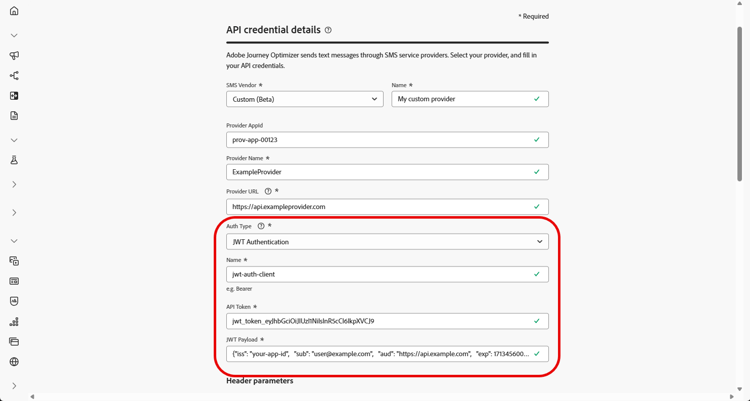
建立API認證後,請完成JWT驗證所需的欄位:
-
名稱:輸入JWT驗證組態的名稱。
-
API Token:輸入您的SMS提供者提供的API Token。
-
JWT裝載:輸入包含JWT所需宣告的JSON裝載,例如簽發者、主體、對象和到期日。
作法影片 video
This section contains structured knowledge intended to support interpretation, retrieval, and question answering related to this topic.
For complete understanding, this information should be combined with the documentation on this page. Neither source is intended to stand alone; the page describes the feature, while this section provides additional context that helps disambiguate terminology, intent, applicability, and constraints.
- TL;DR: This page explains how to integrate a custom messaging provider in Journey Optimizer by creating API credentials, choosing an authentication method, and configuring headers, payloads, mTLS, and inbound settings to send SMS and RCS messages beyond the default Sinch, Twilio, and Infobip options.
Intents:
- Create a custom provider API credential with SMS vendor set to Custom
- Choose and complete an authentication method (API key, MAC, OAuth, or JWT)
- Configure HTTP headers and the Provider Payload for the request
- Enable mTLS support for mutual client and server authentication
- Route a credential’s inbound SMS to a custom dataset
- Verify the SMS connection by sending a sample message to a designated device
Glossary:
- Custom provider: A third-party messaging provider integrated beyond the default options (Sinch, Twilio, and Infobip) by selecting Custom as the SMS vendor (product-specific)
- Provider Payload: The request payload used to validate and customize requests, later used during RCS content design (product-specific)
- Channel Type: An optional classification (SMS, RCS, or MMS) written to XDM experience events for reporting and tracking by channel (product-specific)
- mTLS support: An option ensuring that both the client and server authenticate each other before establishing a secure connection (product-specific)
- Verify SMS connection: An action that tests and verifies the API credentials by sending a sample message to a designated device (product-specific)
Guardrails:
- You can add up to 10 custom header parameters.
- The Content-Type and Charset header fields are set by default and cannot be deleted, though the default Content-Type value can be edited.
- mTLS applies only to the SMS provider (message sending) endpoint; the OAuth token endpoint must not use mTLS and mTLS must be disabled on the token endpoint before testing.
- With Basic or Bearer authentication, the authOption parameter must be included in the JSON payload, and the Provider Payload must reference the template variables {{fromNumber}}, {{toNumber}}, and {{message}}.
- The custom inbound dataset schema must be XDM ExperienceEvent, include the Adobe CJM ExperienceEvent Message interaction details, Message Execution Details, and Message Profile Details field groups, and be enabled for Profile.
- Do not reuse the same API credentials, webhooks, or provider callback URLs (including RCS agents) across sandboxes; create separate agent configurations for each sandbox.
Terminology:
- Canonical name: Custom provider — Acronym: n/a — variants: custom messaging provider, custom SMS provider, Bring Your Own Provider
- Do not confuse: “SMS provider (message sending) endpoint” (uses mTLS) ≠ “OAuth token endpoint” (must not use mTLS)
- Do not confuse: “API key” ≠ “MAC authentication” ≠ “OAuth authentication” ≠ “JWT authentication” (the four Auth Type options)
FAQ:
- Q: How many custom header parameters can I add? — Up to 10 custom header parameters.
- Q: Which authentication types are supported? — API key, MAC authentication, OAuth authentication, and JWT authentication.
- Q: Which endpoint uses mTLS? — mTLS applies only to the SMS provider (message sending) endpoint; the OAuth token endpoint must not use mTLS.
- Q: What must the Provider Payload include for Basic or Bearer authentication? — The authOption parameter in the JSON payload, plus references to the template variables {{fromNumber}}, {{toNumber}}, and {{message}}.
- Q: How do I test the credential? — Click Verify SMS connection, fill in the Number and Message fields structured to align with the provider’s payload format, then click Verify connection to send a sample message to a designated device.